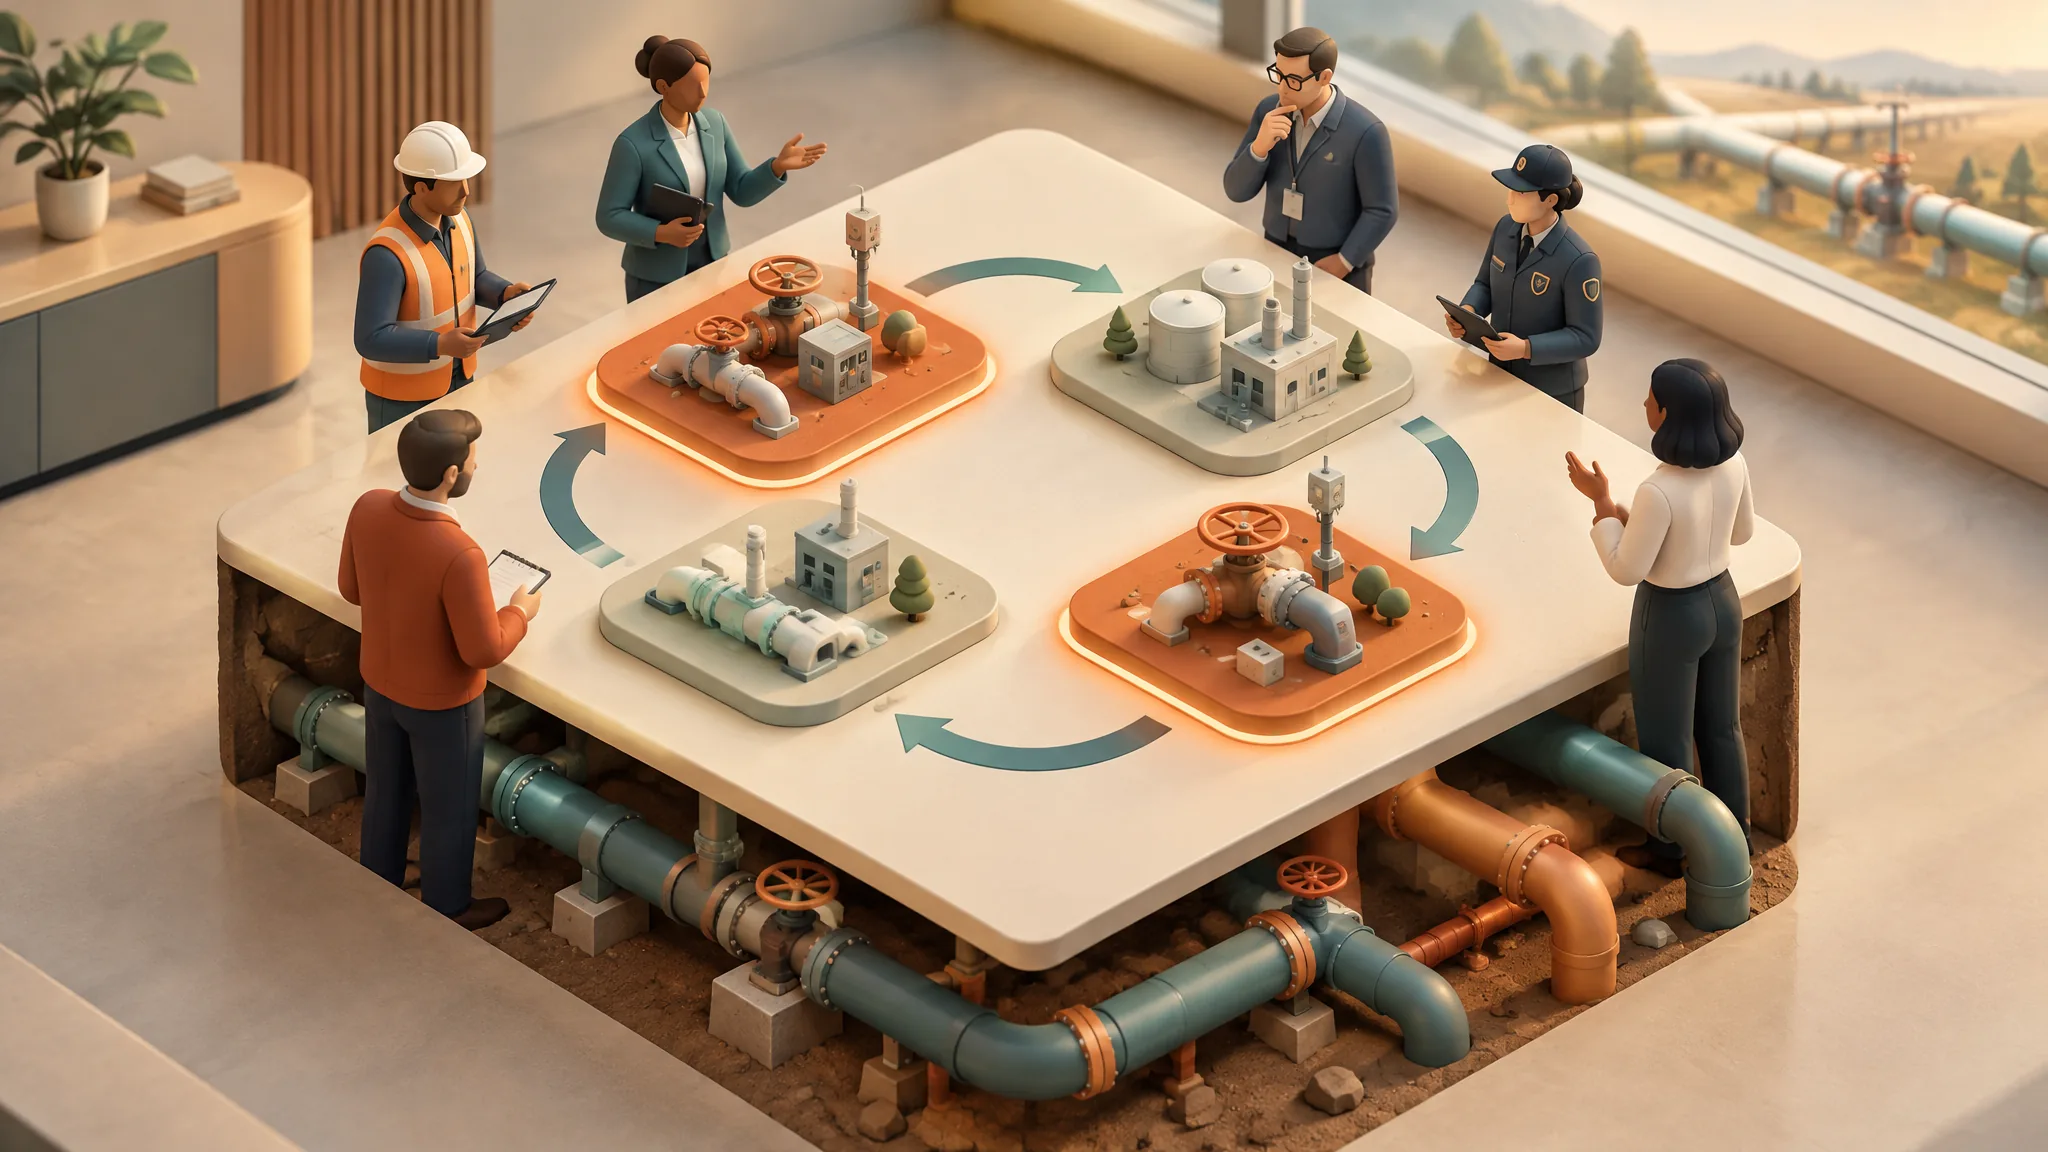
Which two? If your pipeline is one TSA has notified as critical, that question opens your response plan exercise every year, and most teams answer it by checking what they picked last time.
The rule behind the question is short. Your Cybersecurity Incident Response Plan has four objectives. Each year you exercise at least two of them, with the people the plan names taking part. The text does not say which two. Nothing stops you choosing the same pair every year until the directive is retired.
That is how a plan splits in half. Two objectives get rehearsed until they run smoothly. The other two sit in the binder describing steps nobody has timed. You probably know which half yours fall into.
This is written for compliance, OT security and operations staff at an operator TSA has notified under the Pipeline-2021-02 series. If TSA has not notified your company, the directive does not bind you, though the rotation below still works as an internal standard.
What the directive in force actually says
Start with the text, because you can read it. Security Directive Pipeline-2021-02G, listed on TSA's directives page under May 1, 2026, is effective from May 3, 2026 to May 2, 2027. TSA's cover memo says it replaces 02F with "no substantive revisions" and that it is not marked Sensitive Security Information. The testing clause sits in Section III.F, on pages 8 and 9:
"i. Test at least two objectives of the Owner/Operator's Cybersecurity Incident Response Plan required by subparagraphs F.1.a. through F.1.d. of this section, no less than annually; and
ii. Include the employees identified (by position) in paragraph F.2 of this section as active participants in the exercises."
The four objectives, in the directive's order:
- F.1.a, containment. Prompt containment of the infected server or device.
- F.1.b, segregation. Removing infected devices and anything that shared their network, and, the line most plans skip, collecting a forensic memory image of affected devices before powering off or moving them, then labelling every affected piece of equipment.
- F.1.c, backup integrity. Backups secured, stored separately from the system, and free of known malicious code both when the backup is made and when it is tested for restoral.
- F.1.d, IT and OT isolation. An established capability, and governance, for isolating the IT and OT systems when an incident could disrupt operations.
Item F.1.e, the exercise requirement, also carries a letter, so a quick read can count five objectives. There are four. The fifth item is the test itself.
The clause has also grown over time. SD-02C, from July 2022, required annual exercises of the plan and stopped there. Dragos reported that 02D, in July 2023, added the two-objective test and the named participants. The 02F text and the 02G text carry that clause word for word.
Four objectives, two per year: a two-year cycle if you plan one, and no cycle at all if you do not.
Does your plan name a person, by position, for every row in that table? If not, the rotation has already found something.
"We test the same two every year, and nobody has complained"
"We test notification and the call tree under containment, and backup restore, every year. It passes. The directive says two. Why would I volunteer to test the ones that might fail, and then have to write that failure down?"
Because the plan is required to cover all four. The same section says the plan "must provide specific measures sufficient to ensure" objectives a through d, as applicable. Testing two does not excuse the other two from working. It only means you have no record of whether they do.
The directive already thinks in rotations elsewhere. The Assessment Plan in Section III.G must cover at least one-third of the Implementation Plan's measures each year, and all of them over any three-year period. That schedule covers the Implementation Plan, not the response plan, but the pattern is the same: coverage over time, not one slice forever.
A failure written down after an exercise is the cheapest one you will ever have.
"I can't pull people off shift for a hypothetical"
"You want my control room operator and two techs gone for half a day to talk about a cyber scenario? I have nominations to hit and a station that alarms if you look at it wrong. Send me the minutes."
The minutes route is the one the directive closes. The clause asks for the named positions "as active participants," and a stand-in from the compliance office is not the position the plan names. Sending someone who would not do the work on the day does not fit that wording.
What the supervisor can control is the shape. Neither year needs half a day of everyone.
- Run the year one tabletop at shift handover. Both crews are on site. Ninety minutes covers one isolation decision and one containment hour if the facilitator keeps the injects tight.
- Split year two by objective. The memory image drill needs one technician and a spare workstation for about an hour. The restore drill can run on a bench over a day without anyone from the control room until the final check.
- Name the alternate in writing. If the plan lists a position, the plan should say who covers it on nights and weekends. Exercise the alternate in one of the two years.
One detail from objective F.1.b tends to land well with operations. The directive wants a memory image taken before a device is powered off. The instinct on the floor, when a screen behaves strangely, is to reboot it. The bench drill exists to retrain that instinct on a spare HMI, not a live one.
"Why plan two years against a directive that expires in May?"
"02G runs out on May 2. TSA has been writing a permanent rule for two years. By the time year two of your table comes round, the requirement could look completely different."
It could. The history is the best guide. The two-objective clause has carried through every renewal since 02D, and the 02E, 02F and 02G texts word it identically. TSA called the 02G renewal one with no substantive revisions.
The permanent rule is the bigger unknown. TSA proposed it in November 2024 as Enhancing Surface Cyber Risk Management, and 02G's own footnote says TSA still "intends to permanently codify these requirements," so as of May 2026 it was not final. The proposed pipeline section, 1586.227, keeps the same test: at least two objectives a year, named positions as active participants. It adds two clocks: update the plan within 90 days of the exercise, and notify TSA of plan changes within 15 days.
It also regroups the objectives. The proposal folds containment and segregation into one item, which leaves three objectives instead of four. Two of three per year would make the rotation shorter, not longer.
The question worth asking in year one
Which two, then? Not the two that passed last time. The two you have the least evidence for, run with the people who would actually be doing the work at three in the morning.
The directive gives you a floor and a calendar. The rotation turns them into coverage. After two years you hold four records instead of the same two records twice, and each one shows the objective, the scenario, who took part, what failed and what changed afterwards. Whether a record like that ends up as evidence is for TSA to judge. Whether your isolation order works at shift change is something only you can find out.
Sources: TSA, SD Pipeline-2021-02G and transmittal memo, May 1, 2026 | TSA, Security Directives and Emergency Amendments | TSA, SD Pipeline-2021-02F | TSA, SD Pipeline-2021-02C | Dragos, on SD Pipeline-2021-02D | Federal Register, Enhancing Surface Cyber Risk Management, proposed rule, November 7, 2024